By Peace Udugba
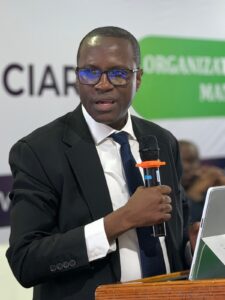
As cybercriminals become increasingly sophisticated, exploiting both technological vulnerabilities and human trust, financial institutions and their customers must strengthen their defences against growing cybersecurity threats, the Chief Information Security Officer of Union Bank of Nigeria, Francis Mojoyinola, has said.
Mojoyinola, who made this known in an article marking the end of Cybersecurity Awareness Month in October, stressed that cybersecurity goes beyond installing sophisticated security systems, noting that human behaviour remains a critical factor in preventing cyberattacks.
In the article titled “The Human Firewall – Why the First Line of Defence Runs in Both Directions,” he explained that cybercriminals increasingly target individuals within and outside organisations through deception, social engineering and manipulation.
According to him, many victims of cyber fraud are not necessarily careless individuals but capable and busy people who mistakenly believe they are too experienced or security-conscious to fall victim to scams.
He noted that although technology plays an important role in cybersecurity, criminals often combine technical weaknesses, stolen credentials and human trust to execute successful attacks.
Citing the 2026 Verizon Data Breach Investigations Report, which examined more than 31,000 security incidents across 145 countries, Mojoyinola said the human element featured in 62 per cent of data breaches, compared with 60 per cent in the previous year.
He observed that as technological security improves, cybercriminals increasingly focus on manipulating people into providing access to protected systems and information.
On the effectiveness of cybersecurity awareness programmes, the Union Bank executive referenced research by the University of California, San Diego, which examined phishing awareness among more than 19,500 employees of a large healthcare system.
He said the eight-month study found that embedded training following failed phishing simulations reduced the likelihood of employees clicking on malicious links by about two per cent, while conventional annual mandatory training showed no meaningful relationship with employees’ susceptibility to phishing attacks.
Mojoyinola, however, maintained that cybersecurity awareness remains important, explaining that training must prepare people to recognise threats in real-life situations, particularly when they are distracted, under pressure or responding to messages supposedly from senior officials.
He also warned that overconfidence could increase vulnerability to cyberattacks, as individuals who believe they cannot be deceived may become less cautious and ignore warning signs.
Insider Threats and Social Engineering
Speaking on cybersecurity risks within financial institutions, Mojoyinola cited figures from the Nigeria Inter-Bank Settlement System (NIBSS), which showed that digital payment fraud losses in Nigeria declined by 51 per cent in 2025 to ₦25.85 billion, from ₦52.26 billion recorded in the previous year.
While acknowledging the improvement, he said social engineering and insider abuse remained significant concerns in the financial sector.
He quoted the NIBSS Chief Executive Officer, Premier Oiwoh, as saying that investigations had confirmed a high level of insider involvement in reported fraud cases.
According to Mojoyinola, insider threats do not always involve dishonest employees, as innocent workers can also become victims of manipulation when fraudsters impersonate senior officials or create situations that demand urgent action.
He emphasised the importance of creating a workplace culture where employees can promptly report mistakes or suspicious activities without fear of punishment.
He explained that the speed with which an employee reports compromised credentials or an unusual transaction could determine the extent of financial and operational damage.
Mojoyinola added that financial institutions must also encourage transparency and information sharing to prevent criminals from exploiting weaknesses across the banking industry.
Customers Also Face Growing Cyber Risks
The Union Bank executive said customers’ banking credentials, including passwords, Personal Identification Numbers (PINs) and One-Time Passwords (OTPs), remain attractive targets for fraudsters.
He warned against sharing confidential banking information with relatives, friends, assistants or individuals claiming to represent financial institutions.
According to him, even arrangements based on trust, such as allowing family members or assistants to handle banking transactions, could increase the number of people with access to sensitive account information and create opportunities for fraud.
He further noted that cybercriminals were increasingly exploiting mobile communication channels, including telephone calls and text messages.
Citing the Verizon report, he said phishing simulations showed that the median click rate for mobile channels, including voice calls and text messages, was about 40 per cent higher than that recorded for email.
He urged customers to remain cautious when receiving unexpected calls or messages requesting urgent financial action or confidential banking details.
Mojoyinola also stressed that banks must treat customers who fall victim to fraud with understanding and respond promptly to reports of suspicious transactions.
He warned that blaming victims could discourage them from reporting incidents quickly, potentially increasing financial losses.
He added that financial institutions must recognise that their reputations could be affected whenever customers are defrauded, even when the initial compromise occurs outside the bank’s systems.
Five Essential Cybersecurity Habits
Mojoyinola identified several practical measures individuals and employees should adopt to reduce their exposure to cybercrime.
These include treating urgent financial requests with suspicion, never sharing authentication codes received on mobile phones, verifying unusual requests through trusted communication channels, refusing authentication prompts they did not initiate and reporting suspicious activities immediately.
He advised customers to contact their banks through official telephone numbers or verified mobile applications rather than relying on contact details or links supplied by unknown callers.
He maintained that customer education should be a continuous exercise rather than a campaign limited to Cybersecurity Awareness Month.
Union Bank Advocates Cyber-Strong Culture
Speaking on the need for stronger institutional safeguards, Mojoyinola said financial institutions must complement awareness programmes with effective security technologies and internal controls.
He identified multi-factor authentication, password managers, restricted access privileges, additional approval procedures and continuous transaction monitoring as important measures for reducing cybersecurity risks.
According to him, institutions must develop systems capable of containing individual mistakes rather than relying entirely on employees and customers to maintain perfect vigilance.
He disclosed that Union Bank of Nigeria adopted “Building a Cyber Strong Culture” as its theme for this year’s Cybersecurity Awareness Month.
He explained that the theme reflects the bank’s belief that cybersecurity is not solely about purchasing and installing security technology but also about developing responsible behaviour and a culture of vigilance across the organisation.
Mojoyinola said a cyber-strong culture encourages employees to question unusual instructions, customers to report suspicious activities and institutions to design security systems around real human behaviour.
He added that employees and customers should be regarded as essential participants in cybersecurity rather than the weakest links in the security chain.
He concluded that while security technologies would continue to improve and cybercriminals would continue to devise new methods, a colleague who promptly reports a security breach and a customer who raises an alarm before a fraudulent transaction is completed could make a significant difference.
About the Author
Francis Mojoyinola is the Chief Information Security Officer of Union Bank of Nigeria, where he leads the bank’s cybersecurity strategy, information security governance and data protection operations.
He has more than two decades of experience in information technology, risk management and financial control within the Nigerian banking industry.
He is a Fellow of the Institute of Chartered Accountants of Nigeria (FCA), an Honorary Senior Member of the Chartered Institute of Bankers of Nigeria (HCIB) and a Certified Information Security Manager (CISM). He is also a graduate of Obafemi Awolowo University, Ile-Ife.